
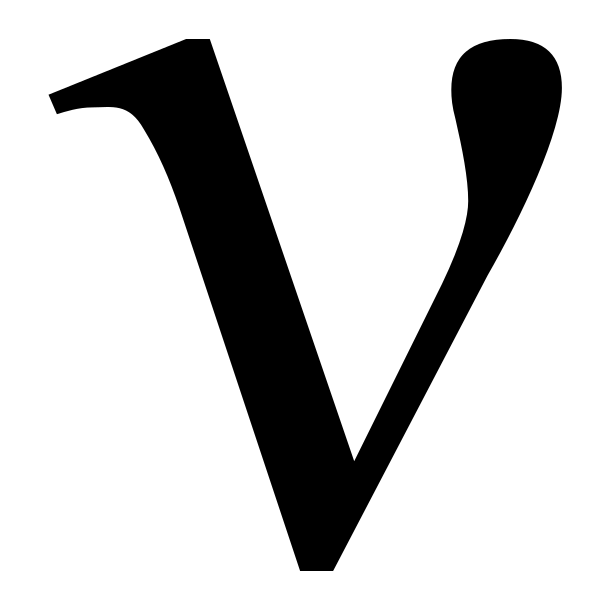
 Nu
sandbox container. It can
see Nu’s workspace, ~/.nu/workspace, and read its skills and packages. It
can’t see Nu’s secrets, policy, or database.
The container’s filesystem is read-only outside the workspace, it runs without
Linux capabilities, and it has 4 GB of memory.
Installing tools
The sandbox hasnode, npm, git, gh, curl, and rg. Nu can install
other tools into its home folder, ~/.nu/workspace/.home, where they last
across restarts. npm install -g installs there, and ~/.local/bin is on the
PATH.
To build tools into the sandbox instead, give it your own image in
~/.nu/compose.override.yaml:
docker compose build sandbox after each update so the image picks up the
new version.
Working on other folders
To let Nu work on a folder outside the workspace, mount it into the sandbox at the same path it has on your machine. Add it to the sandbox’svolumes in
~/.nu/compose.override.yaml:
Sharing secrets
Secrets stay out of the sandbox, and work that needs one runs as a tool instead. When a command does need a secret, such as a GitHub token forgit push, share it:
GITHUB_TOKEN or GH_TOKEN shared, git and gh work against GitHub.
Commits are authored as the token’s GitHub account, using its private noreply
email address.
Other sandboxes
An extension can run the workspace somewhere else, such as a cloud sandbox provider, by registering a sandbox:
Each of Nu’s services loads the extension, so the sandbox must reach the same
workspace from all of them. Nu reads skills and long command output from its
own disk, wherever the sandbox runs. Packages in a sandbox like this are saved
with
package_write, since Nu can’t install them from a path it can’t see.